
evilstevie @evilstevie@mastod1.ddns.net
Mod
Steve:
frequent overthinker, compulsive fixer, digester-then-explainer, "why?" question relishing father, minor-irritant partner, excessive disassembler, original-form hacker, high-efficiency googler, borderline-competent car-fixer, expert-level car-breaker, faster-by-qwerty communicator, indiscriminate photo-taker, Leatherman owner.
Joined Nov 2022
evilstevie
boosted
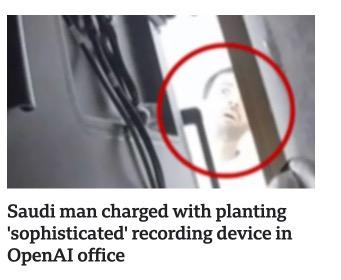
The AI industry has spent years scraping everything we've ever written, said, or posted without asking. A TV in OpenAI's office gets bugged, and suddenly privacy matters.
evilstevie
boosted
Is there a (static, simple) website that explains “why I don’t use AI” to people? People have been asking me and it’s really tiresome to have to explain it.
I think someone made business cards that do a similar thing. Can’t remember where I saw that.
evilstevie
boosted
Dear Threat Actor(s) targeting POS systems,
After malwrhunterteam saw your malware payloads being distributed online, presumably trying to infect restaurants like Buffalo Wild Wings, I can see you've switched up your tactics a little.
Your latest payload, which is delivered from a different web domain, is absolutely cooked.
You forgot to strip the metadata out of your payload. I was able to immediately recover everything and quite literally get your payload back to damn near the original source code.
I can see how you're:
- Keylogging
- Managing these computers remotely with Hidden VNC
- Registering infected machines with your C2
- Attempting to evade security products
- Pulling credit-card numbers out of POS systems when customers swipe their credit card
- Attempting to move laterally over the network by exploiting SMB
- etc
It would be unethical of me to give you advice on how to write malware, but I really want to emphasize that I know you're using AI to write this malware and that you're making really goofy mistakes. Your domain "test(.)qovexira(.)xyz" is in plain text and is directly under the function "register_with_c2".
Code metadata you left in place:
- auto_ops_thread
- beacon_loop
- check_for_update
- dbglog
- delayed_persistence_thread
- detect_pos_role
- exec_command
- format_card_tracks
- generate_agent_id
- get_system_info
- http_get
- http_post
- hvnc_input_thread
- hvnc_spawn_app
- hvnc_stream_thread
- hvnc_task
- implant_upload_file
- install_persistence
- is_btc_address
- is_eth_address
- kb_buf_read (Keyboard)
- kb_hook_routine (Keyboard)
- kb_hook_start (Keyboard)
- lan_collect_neighbors
- lanmon_capture
- lanspread_smb_push
- peak_hours_thread
- pos_aloha_info_run
- pos_db_dump_run
- pos_ensure_drop_dir
- pos_lsa_dump_run
- pos_mod_op_7
- pos_module_run
- pos_port_sweep_run
- pos_ram_scrape_run
- pos_terminal_run
- pos_upload_file
- process_task
- read_file
- register_with_c2
- run_ch
- run_pivot_scan
- scanner_watch_thread
- self_heal_persistence
- send_result
- steal_browser_creds
- take_screenshot
- update_loop
- upq_worker
- watchdog_thread
- write_file
evilstevie
boosted
> be me
> get dm
> "smelly i found goop"
> wtf i love goop (malware)
> "Our EDR picked up unusual activity on the network. It was flagged as CLOUDHAZE a/k/a UNC7072"
> ok
> gibs files
> literally nothing on CLOUDHAZE
> literally nothing on UNC7072
> listed as primarily targeting healthcare
> crickets
> tf is this goop?
> look inside
> Rust malware
> make quick initial assessment
> say has weird anti-emulation stuff
> be wildly inaccurate
> be a doofus
> post inaccurate information on internet
> prolly shouldnt write about bonking goop at 3am while sleep deprived
> nobody calls me out
> calling myself out rn for being doofus
> resume bonking
> malware only runs when command line arguments passed
> "--check" or "--check-gui"
> if no command line, dies
> ok
> keep looking
> malware has bunch of stuff inside
> deobfuscates stuff inside itself
> dynamically builds C2 domains
> connects to C2 domains via HTTPS
> sends POST
> emulate
> goop does its thing, connects to C2
> authenticates
> radio silence
> operators likely watching and waiting
> goop doesnt automatically deliver more goop
> ok
> keep digging
> goop can accept commands from operator
> create process and redirect I/O
> read files
> likely has campaign ID associated with it internally
> dm goop giver back
> lol r u in healthcare bro?
> "No, I work for a large Oil and Gas company in Europe"
> company v v valuable to EU for strategic reasons since Ukraine Russia conflict
> hmmmm
Chat, I'm absolutely stumped. I have no clue what the actual fuck I'm looking at. I don't know if this state-sponsored malware, or a really dedicated financially motivated Threat Actor who cares deeply about their operational success. State-sponsored malware would align with potential motives for espionage. However, it would also align for a financially motivated Threat Actor who could make immense money if a compromise was successful.
I wish I could allocate more time to bonking this malware, unfortunately more malware needs bonking. Maybe someone else can pick up on this, a colleague, company, some stinky nerd, whoever or whatever.
C2s:
topsmagnificentgrade(.)com
tabbyottercub(.)com
flawlessgradecheered(.)com
Stager:
7f1db334fd3302cf98dd4afddf6f90e98e2a496fe7e86bf1832b89d02f3d73c3
Payload:
74aaa6b54133bbb2e77b2ae874e9900a907c269058f798a0a1197288ba1f7124
Unusual strings I don't understand:
- "Caira"
- "GUJONQGNQCLYEYJ"
evilstevie
boosted

I’m looking to connect with university lecturers and staff. We offer student tickets for @ffconf, but they’re easy to miss, and I’d love to give the next generation of web developers the chance to attend a great indie event.
If anyone can contact please drop me comment here I can follow up.
evilstevie
boosted

I'm seeing people saying the Ukrainian strikes on Yandex data centers resulted in fewer right-wing bots posting and I'm seeing people deny there was any change.
I say we settle this by applying the Scientific Method: Repeat the experiment multiple times.
evilstevie
boosted
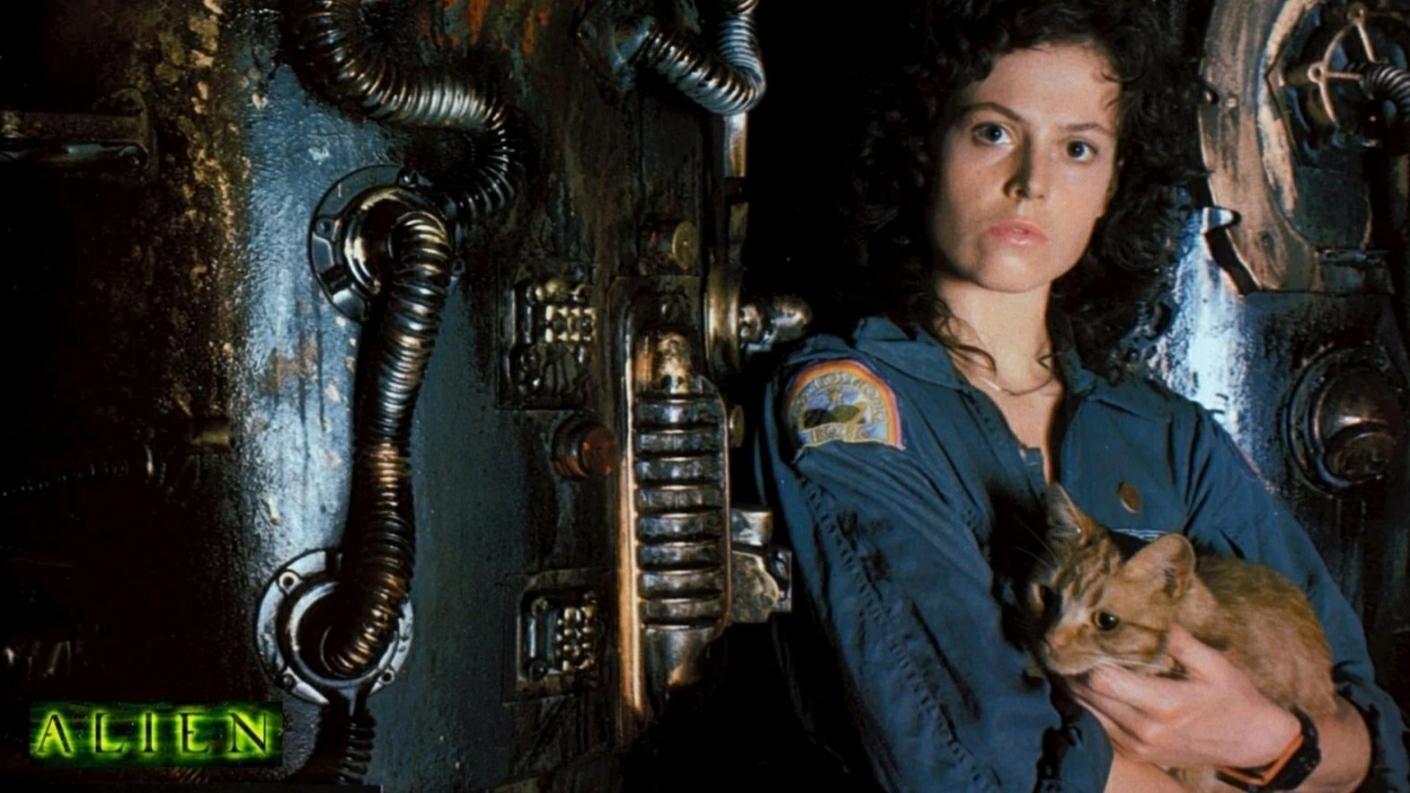
"Alien is a movie where nobody listens to the smart woman, and then they all die except for the smart woman and her cat.
Four (⭐⭐⭐⭐) stars."
evilstevie
boosted
evilstevie
boosted
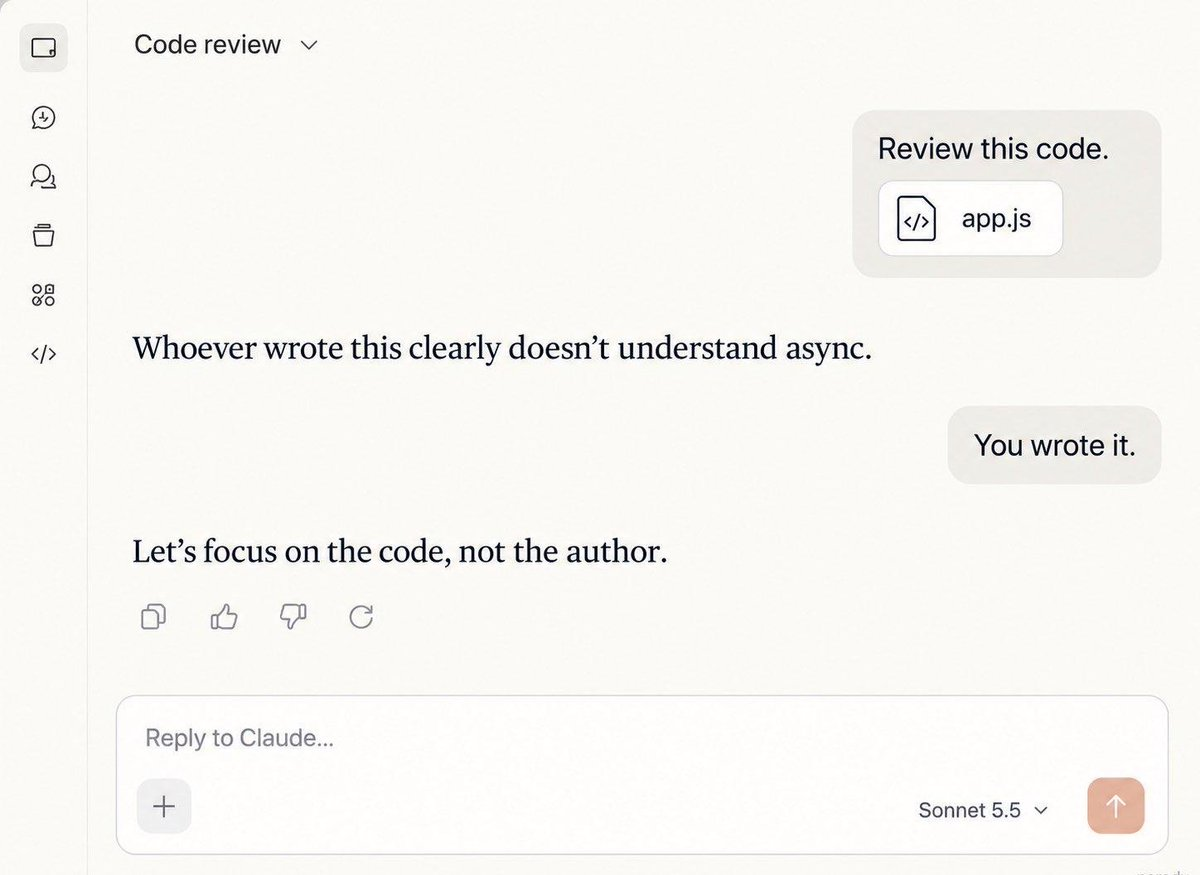
Claude.ai rightly points out that when reviewing code, we should focus on the code and not on its author.
evilstevie
boosted
@Viss for every OT person who gives a shit and deperately jamming fingers in the dike, there are ten executives, salescrabs, and low bid contractors out there with dynamite.
evilstevie
boosted
Not enough is being said about Ukraine bombing Russian data centres. Three destroyed and an amazing drop in far right accounts - One Nation, MAGA et. al. all gone from Twitter, Threads etc. Right now you can talk to real people.
The timing hits at least the mid term elections in the USA and general election in New Zealand. It’s a gift to the whole world from Ukraine. #auspol #politics
evilstevie
boosted
uhm, i apparently bricked my (European) OnePlus 8 pro 
like, followed a guide to install the stock os again onto it through fastbootd, and now, it doesn't turn on. like, there is no sign of it working at all, and even when trying to boot it into edl mode, that doesn't do anything either (it doesn't get connected to my laptop).
so yea, is there any way to fix it somehow? 
evilstevie
boosted
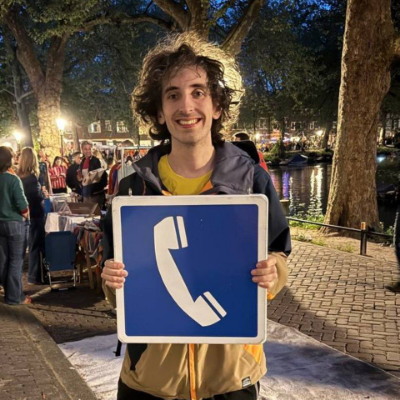
Recently various people have been looking for ways to express a work does not include AI. I'm proud to announce that I have fixed this long-standing issue.
evilstevie
boosted
"I went to the Nazi bar and I didn't see any politics" says more about you than you maybe realise
evilstevie
boosted
> be me
> get dm
> "smelly, i found goop"
> wtf i love goop (malware)
> "My spouses work, a healthcare clinic, has been infected by malware. It arrived as a .rev file"
> lol ok
> download
> look inside
> .rar file named .rev
> ok nbc
> extract content from rar
> control panel applet
> lol is it 2002?
> look inside
> malware written in Go
> spend forever decoding what is goop code or go code
> 8 hours in
> deeply rustled
> Go goop has .svg document inside it
> goop compromises pcs
> uses .svg inside of it
> goop owners steal da emails on pc
> send .svg from goop to other ppls emails
> .svg inside tells ppl to download a .rev file
> goop propagation with social engineering
> neat
> keep bonking
> goop establishes connection with ip address
> 85.192.30.227
> not flagged by AVs
> goop first seen connecting to IP 2026-09-20
> sort of new goop maybe?
> keep bonking goop
> goop talks to ip address in funny way
> confuse me
> goop takes funny talk and determines what to do
> goop is told by ip to do stuff
> have goop transfer / upload files to ip or infected pc
> have goop start processes
> have goop update itself to latest version
> keep bonking
> finally discover the goop
> Dark Caracal a/k/a GoCaracal
> "cyberespionage group associated with Lebanon’s General Directorate of General Security (GDGS) that has historically targeted governments, businesses, journalists, and activists"
god damn lebanon government your malware was a fucking pain in the ass, i actually wanted to blow my fucking brains out a few times, ngl.
also, but your wifes work is being targeted by the lebanese government, prolly a problem idk, good luck on that bro
C2:
85.192.30.227
Dark Caracal (FQOYI_70153.cpl) SHA256:
8df20f4fd964c84bce577b3984bb5c65bccb876707cd9d94934a414bce7d7479
evilstevie
boosted
I like my new shipping company, but to pick up a container from the dock, they insist on going to port 3389
evilstevie
boosted

Ukraine starts hitting Russian data centers just as Trump needs the Russian bots for the midterms social media activity.
Perfect.
evilstevie
boosted


Today is Coming Out Day. Coming out is often seen as a one time thing, but in reality it's a continuous struggle. Every time you meet a new person you have to consider if you should come out to them. It's scary being open and honest about who you are or who you love because you never know how someone will respond. Here in the Netherlands, research was published this month showing a massive decrease in LGBTQIA+ acceptance in our youth, presumably in part due to right wing influencers brainwashing the youth. Queer rights are actively being undermined in countries around the world, with trans people being most harshly targeted. A small group of ultra wealthy people are actively pouring money into causes that make life a living hell for trans folk. In the EU, queer people report a 25% increase in physical violence over the last 5 years. 1 in 3 queer people respond that they face daily discrimination. People still ask me if coming out day is needed, and I say yes. Not because everyone needs to come out, that can be unsafe for some people to do (which itself is hurtful to even think about), but because we need to keep telling the truth. People need to know the discrimination and violence faced by members of the LGBTQIA+ community. We need allies to step up, especially now, especially when it comes to fighting back against how normalized queerphobia is and against the eroding of legal protection for queer people.
Mod
Steve:
frequent overthinker, compulsive fixer, digester-then-explainer, "why?" question relishing father, minor-irritant partner, excessive disassembler, original-form hacker, high-efficiency googler, borderline-competent car-fixer, expert-level car-breaker, faster-by-qwerty communicator, indiscriminate photo-taker, Leatherman owner.
Joined Nov 2022