
evilstevie @evilstevie@mastod1.ddns.net
Mod
Steve:
frequent overthinker, compulsive fixer, digester-then-explainer, "why?" question relishing father, minor-irritant partner, excessive disassembler, original-form hacker, high-efficiency googler, borderline-competent car-fixer, expert-level car-breaker, faster-by-qwerty communicator, indiscriminate photo-taker, Leatherman owner.
Joined Nov 2022
evilstevie
boosted

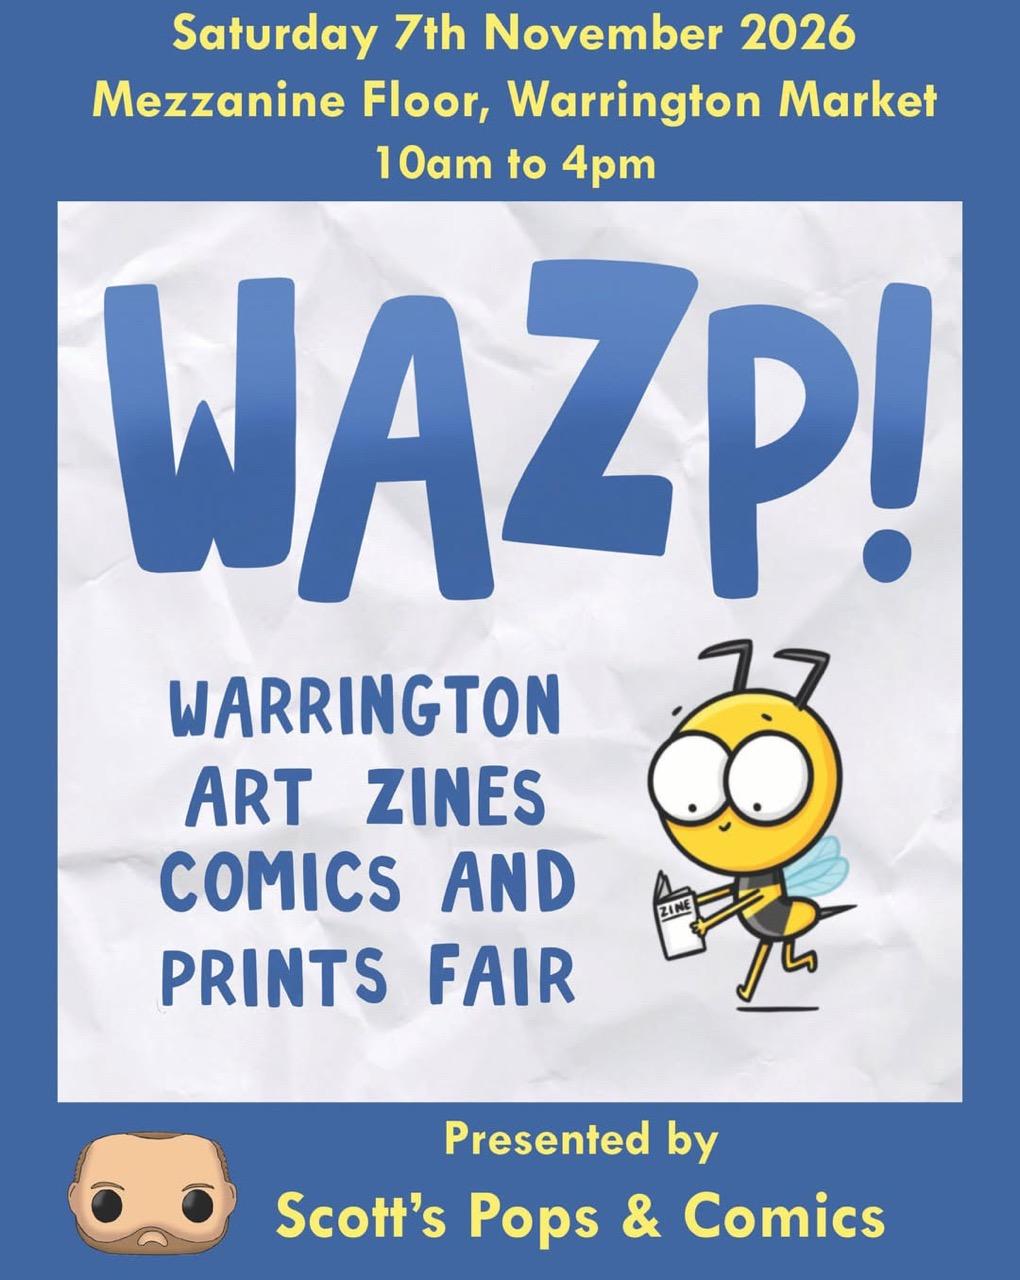
7th November Warrington Market.
One one hand, I could say I’ve got the bug for having a table at art fairs because it was a lot of fun. And, on the other hand, I could say that I got a lot of things printed and didn’t sell very much at my first event so need to do more.
Both things can be true.
evilstevie
boosted
This isn't even the queerest conversation in Kitsune Tails, currently 35% off! https://kitsunegames.com/kitsunetails
Or help our queer studio survive the year by getting four games bundled for $17.99 on itch (https://itch.io/s/204320/kitsune-games-fall-sale-2026-part-2) or $18.75 on Steam (https://store.steampowered.com/bundle/15673/Kitsune_Games_Complete_Pack/)
Bundle contents in the reply ⬇️
evilstevie
boosted
sorry for all the promotional posts but i gotta run and promote steam sales as often as i can for our studio to survive the next few months and that happened to create two back to back steam sales cause of the fall sale 🙃
evilstevie
boosted
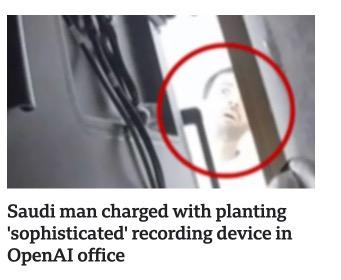
Sam Altman is upset someone left a recording device in his conference room. I guess he forgot to explicitly opt out of data collection for marketing and training purposes
evilstevie
boosted

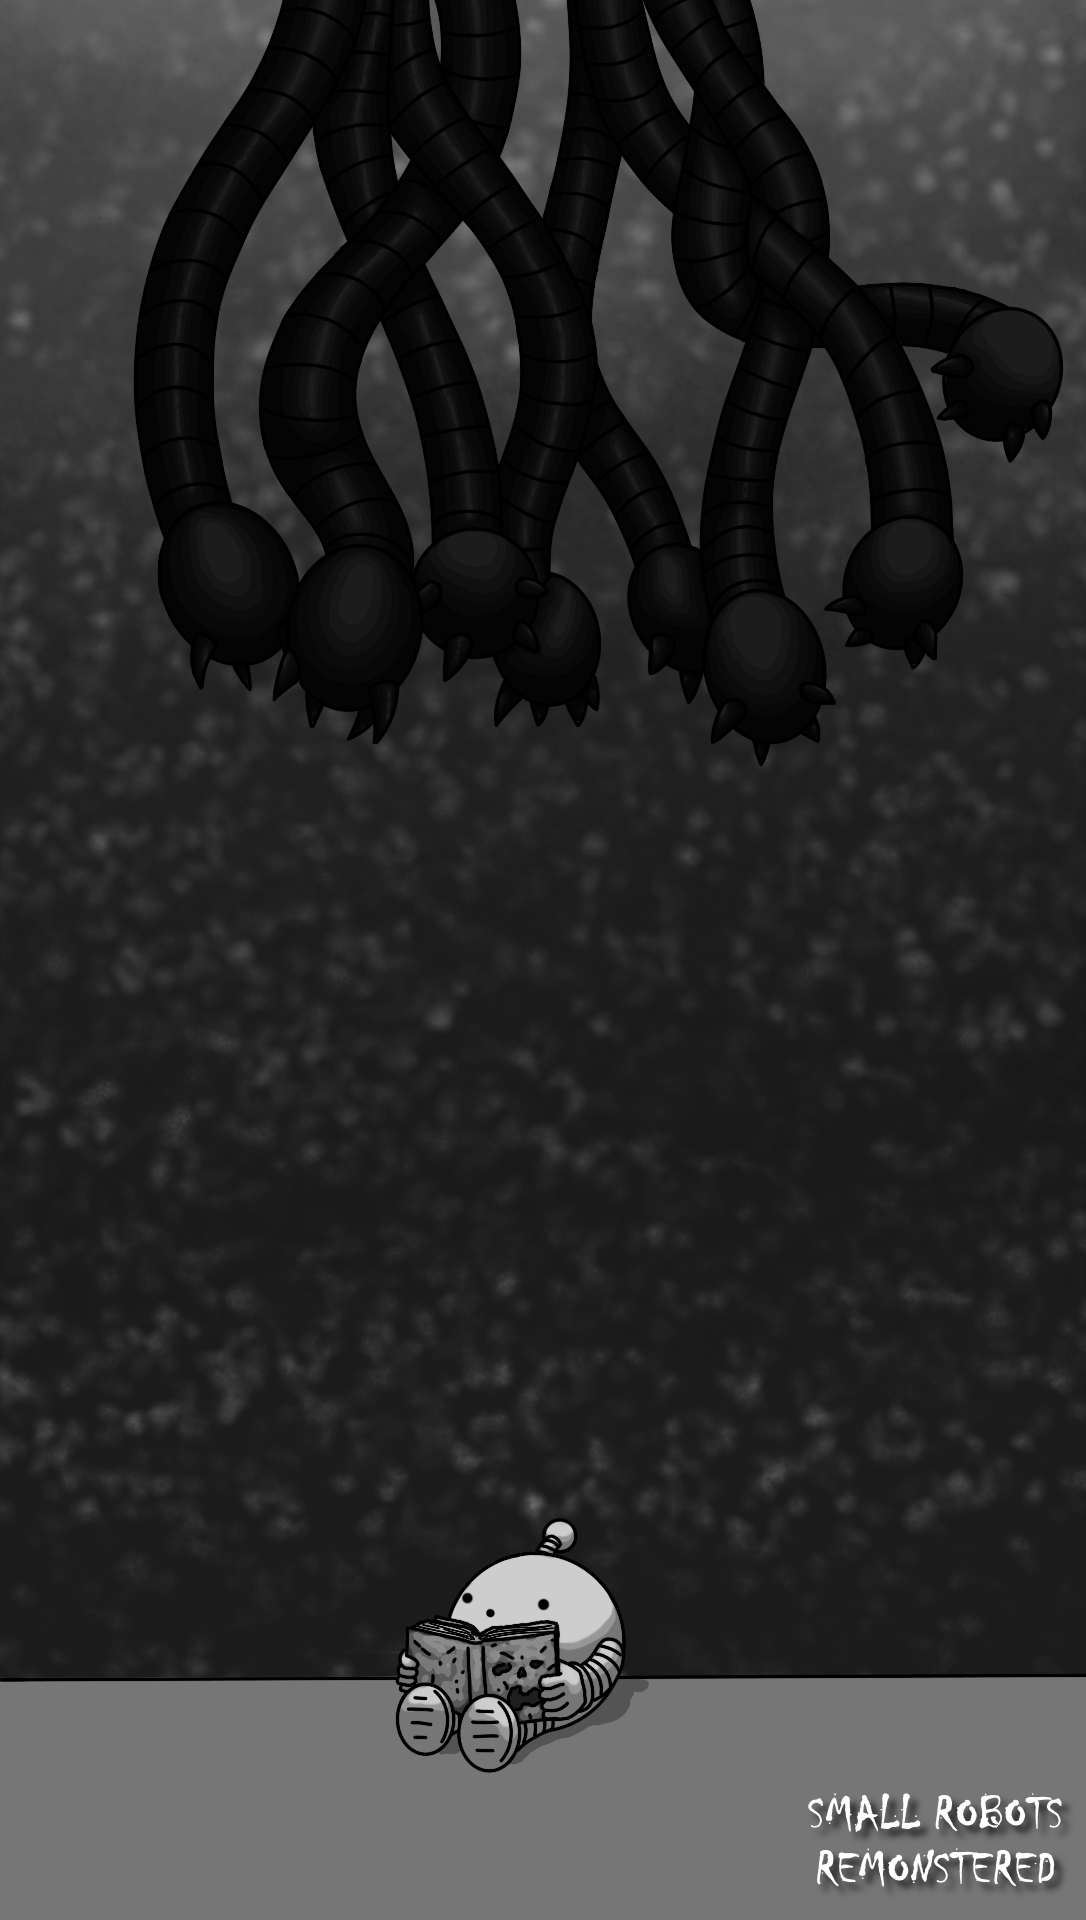
1870) Warlockbot. Is about to forge a pact with a nigh-omnipotent otherworldly entity in exchange for temporal power: with hilarious results! #SmallRobotsRemonstered #Halloween
evilstevie
boosted
Anybody interested in a free ride in a helicopter, flight for 4 people?!
I'm still looking for 2 more people to join us. We leave early Saturday (October 24th) morning from Manchester and will fly to Poole in Dorset where we will have breakfast and then on a yacht for lunch.
Then we’ll have a flight to Jersey and return to Poole for dinner, then fly back home.
If interested please DM me. Preferably someone with a helicopter and yacht, otherwise we can't go.
evilstevie
boosted
The AI industry has spent years scraping everything we've ever written, said, or posted without asking. A TV in OpenAI's office gets bugged, and suddenly privacy matters.
@drahardja my partial reasoning is:
I've already part-trained a new intelligence. it's going so well that mrs evilstevie says "it's like there's two of you, ffs"
this sounds like a problem I shouldn't repeat.
and the other bit is that it's dragstrip-racing levels of resource consumption being used for going-round-the-neighbour results, and I really reeeeally want my computing efficient (to the level of gui animations and transparencies being disabled if I have to gui)
evilstevie
boosted
Is there a (static, simple) website that explains “why I don’t use AI” to people? People have been asking me and it’s really tiresome to have to explain it.
I think someone made business cards that do a similar thing. Can’t remember where I saw that.
evilstevie
boosted
Dear Threat Actor(s) targeting POS systems,
After malwrhunterteam saw your malware payloads being distributed online, presumably trying to infect restaurants like Buffalo Wild Wings, I can see you've switched up your tactics a little.
Your latest payload, which is delivered from a different web domain, is absolutely cooked.
You forgot to strip the metadata out of your payload. I was able to immediately recover everything and quite literally get your payload back to damn near the original source code.
I can see how you're:
- Keylogging
- Managing these computers remotely with Hidden VNC
- Registering infected machines with your C2
- Attempting to evade security products
- Pulling credit-card numbers out of POS systems when customers swipe their credit card
- Attempting to move laterally over the network by exploiting SMB
- etc
It would be unethical of me to give you advice on how to write malware, but I really want to emphasize that I know you're using AI to write this malware and that you're making really goofy mistakes. Your domain "test(.)qovexira(.)xyz" is in plain text and is directly under the function "register_with_c2".
Code metadata you left in place:
- auto_ops_thread
- beacon_loop
- check_for_update
- dbglog
- delayed_persistence_thread
- detect_pos_role
- exec_command
- format_card_tracks
- generate_agent_id
- get_system_info
- http_get
- http_post
- hvnc_input_thread
- hvnc_spawn_app
- hvnc_stream_thread
- hvnc_task
- implant_upload_file
- install_persistence
- is_btc_address
- is_eth_address
- kb_buf_read (Keyboard)
- kb_hook_routine (Keyboard)
- kb_hook_start (Keyboard)
- lan_collect_neighbors
- lanmon_capture
- lanspread_smb_push
- peak_hours_thread
- pos_aloha_info_run
- pos_db_dump_run
- pos_ensure_drop_dir
- pos_lsa_dump_run
- pos_mod_op_7
- pos_module_run
- pos_port_sweep_run
- pos_ram_scrape_run
- pos_terminal_run
- pos_upload_file
- process_task
- read_file
- register_with_c2
- run_ch
- run_pivot_scan
- scanner_watch_thread
- self_heal_persistence
- send_result
- steal_browser_creds
- take_screenshot
- update_loop
- upq_worker
- watchdog_thread
- write_file
evilstevie
boosted
> be me
> get dm
> "smelly i found goop"
> wtf i love goop (malware)
> "Our EDR picked up unusual activity on the network. It was flagged as CLOUDHAZE a/k/a UNC7072"
> ok
> gibs files
> literally nothing on CLOUDHAZE
> literally nothing on UNC7072
> listed as primarily targeting healthcare
> crickets
> tf is this goop?
> look inside
> Rust malware
> make quick initial assessment
> say has weird anti-emulation stuff
> be wildly inaccurate
> be a doofus
> post inaccurate information on internet
> prolly shouldnt write about bonking goop at 3am while sleep deprived
> nobody calls me out
> calling myself out rn for being doofus
> resume bonking
> malware only runs when command line arguments passed
> "--check" or "--check-gui"
> if no command line, dies
> ok
> keep looking
> malware has bunch of stuff inside
> deobfuscates stuff inside itself
> dynamically builds C2 domains
> connects to C2 domains via HTTPS
> sends POST
> emulate
> goop does its thing, connects to C2
> authenticates
> radio silence
> operators likely watching and waiting
> goop doesnt automatically deliver more goop
> ok
> keep digging
> goop can accept commands from operator
> create process and redirect I/O
> read files
> likely has campaign ID associated with it internally
> dm goop giver back
> lol r u in healthcare bro?
> "No, I work for a large Oil and Gas company in Europe"
> company v v valuable to EU for strategic reasons since Ukraine Russia conflict
> hmmmm
Chat, I'm absolutely stumped. I have no clue what the actual fuck I'm looking at. I don't know if this state-sponsored malware, or a really dedicated financially motivated Threat Actor who cares deeply about their operational success. State-sponsored malware would align with potential motives for espionage. However, it would also align for a financially motivated Threat Actor who could make immense money if a compromise was successful.
I wish I could allocate more time to bonking this malware, unfortunately more malware needs bonking. Maybe someone else can pick up on this, a colleague, company, some stinky nerd, whoever or whatever.
C2s:
topsmagnificentgrade(.)com
tabbyottercub(.)com
flawlessgradecheered(.)com
Stager:
7f1db334fd3302cf98dd4afddf6f90e98e2a496fe7e86bf1832b89d02f3d73c3
Payload:
74aaa6b54133bbb2e77b2ae874e9900a907c269058f798a0a1197288ba1f7124
Unusual strings I don't understand:
- "Caira"
- "GUJONQGNQCLYEYJ"
@anon_opin depends if they are an in-sentence list or branched options, in my brain.
listing, maybe commas or semicolons,
options, each needs closure.
@Viss "willfully violated" does make it sound quite deliberate rather than a slip of KYC measures...
@hailey burn it down?
evilstevie
boosted

I’m looking to connect with university lecturers and staff. We offer student tickets for @ffconf, but they’re easy to miss, and I’d love to give the next generation of web developers the chance to attend a great indie event.
If anyone can contact please drop me comment here I can follow up.
evilstevie
boosted


I'm seeing people saying the Ukrainian strikes on Yandex data centers resulted in fewer right-wing bots posting and I'm seeing people deny there was any change.
I say we settle this by applying the Scientific Method: Repeat the experiment multiple times.
@munin it does make a change from them being used to install/refresh an ad channel though
Mod
Steve:
frequent overthinker, compulsive fixer, digester-then-explainer, "why?" question relishing father, minor-irritant partner, excessive disassembler, original-form hacker, high-efficiency googler, borderline-competent car-fixer, expert-level car-breaker, faster-by-qwerty communicator, indiscriminate photo-taker, Leatherman owner.
Joined Nov 2022